Your .NET application,
fully reviewed in 5 days
A senior architect reviews your code, architecture, performance and security, then hands you a prioritised roadmap your team can start on the following Monday. Fixed price, no surprises.
It is, if one of these sounds familiar
"Every new feature takes twice as long as it used to."
"The application is getting slower and nobody really knows why."
"We have to move to modern .NET or to the cloud, but where do we start?"
Five areas, each scored
Every area gets a score and concrete recommendations, ranked by impact and by effort.
01 · Architecture
Boundaries, dependencies, coupling, choice of patterns, and how easily the system can evolve.
02 · Code quality
Readability, duplication, test coverage, and technical debt estimated in days of work.
03 · Performance
EF Core queries, data access, async code, caching, and measured hot spots.
04 · Security
Authentication, authorisation, secrets management and vulnerable dependencies.
05 · Operations
CI/CD, observability, cloud infrastructure and hosting costs.
Ranked, not just listed
Each finding comes with its severity, business impact, estimated effort and the recommended fix.
Five days, one deliverable per step
-
Day 1
Kick-off
Interviews with the team, read-only access, goals and constraints.
-
Day 2
Code & architecture
Solution review, static analysis, dependency map.
-
Day 3
Performance & security
Profiling, queries, secrets, permissions and vulnerable dependencies.
-
Day 4
Synthesis
Writing the report and the 6-month roadmap.
-
Day 5
Debrief
2-hour session with the team and management, questions and answers.
Documents made to be used, not filed away
Two offers, two fixed prices
The exact price is confirmed after the scoping call, based on the size of your solution. No overrun after that.
- All five areas: architecture, code, performance, security, operations
- Prioritised report and 6-month roadmap
- 2-hour debrief with your team
- 30 days of follow-up questions by e-mail
- Inventory of exposed secrets: code, pipelines, configuration
- Review of Key Vault access and managed identities
- Prioritised remediation plan
- 1-hour debrief
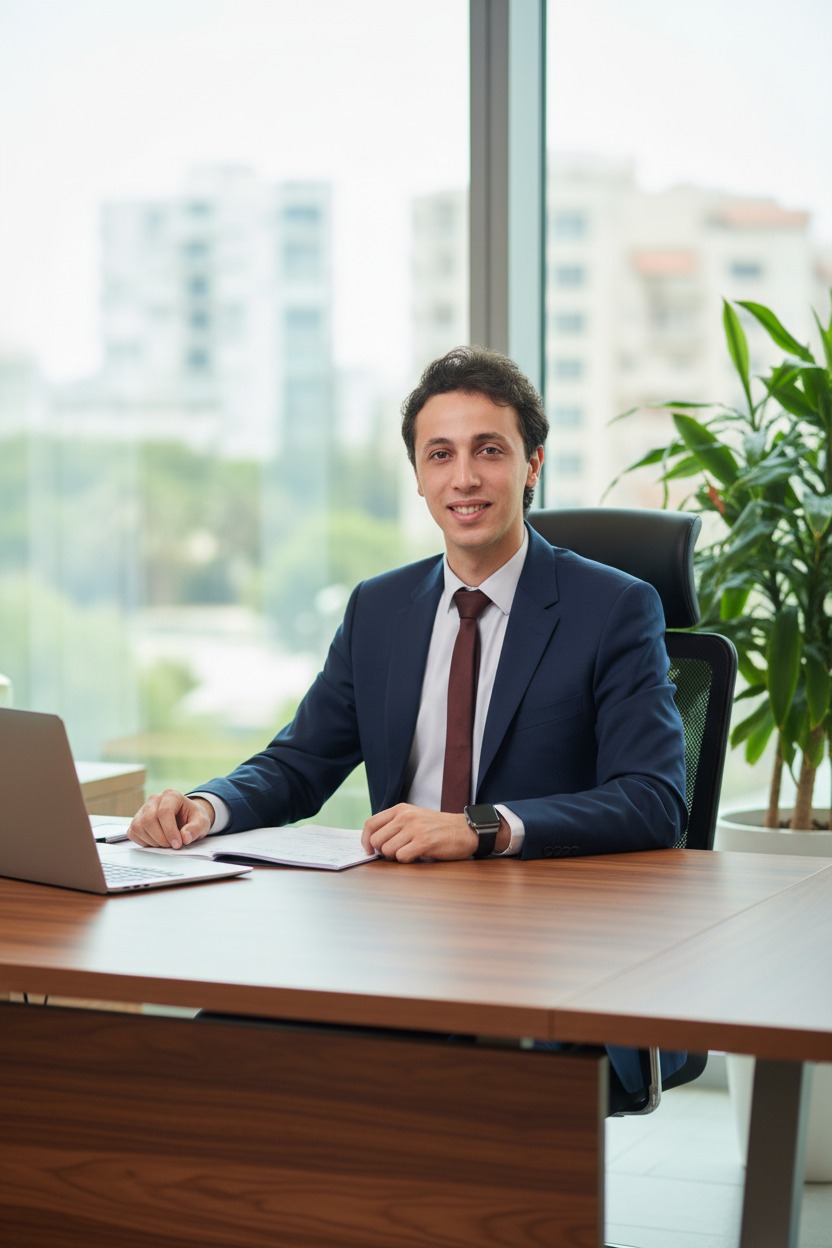
Hakim Khammassi, senior .NET architect
More than 14 years of enterprise software engineering in insurance, banking, energy and European institutions. Founder of PRYZMA and designer of IGETIS KeyVault, a SaaS secrets-management platform. Certified Six Sigma Black Belt: an analytical method you will find in every report.
Frequently asked questions
What access do you need?
Read-only access to the code repository and, if possible, to your monitoring tools. No write access to production, ever.
Our application is not on recent .NET. Is that a problem?
No. .NET Framework applications are a common case; the audit then includes a migration path to modern .NET.
What happens after the audit?
Your team can follow the roadmap on its own. If you wish, PRYZMA can also help you implement it.
Does our code stay confidential?
Yes. A non-disclosure agreement is signed before any access, and no copy of the code is kept after the engagement.
In which language is the report written?
English or French, as you prefer. The debrief can be held in either language too.
20 minutes to know whether the audit will help
A free call, no commitment. At the very least, you leave with a first view on your priorities.